
On October 29, attackers took about $6.34 billion in digital assets from Binance. According to the company's preliminary findings, a fake job interview helped make this happen.
The target of that interview wasn’t an outside applicant but a Binance engineer, reached through a job-platform profile that mentioned the company. Instead of breaking into Binance, the attackers used an employee that said yes to an opportunity. Here’s how the theft unfolded, why the interview mattered, and how to make sure this doesn’t happen at your own company.
Months of groundwork for a few hours of transfer
Attackers used unauthorized access to an internal wallet signing service to start transactions outside Binance’s normal withdrawal process. Hot wallets sent 233.46 million XRP, then SOL, OP, and 18,270 BTC, to addresses the attacker controlled.
Binance’s internal alert fired and the company suspended withdrawals, but that wasn’t enough. The attackers had used Ethereum Improvement Proposal 7702 (EIP-7702) to give a smart contract they controlled partial execution rights over a hot wallet. Those permissions lived on-chain, outside Binance’s withdrawal systems. Because the wallet used multi-party computation (MPC), no single private key could revoke them, so the team built a specialized procedure that took time.
The last transfer was only finalized nearly four hours after the first. Binance says about $2.85 billion was frozen or intercepted, and it cites an FBI alert attributing the attack to North Korea.
It started with an interview that looked like any other
In June, a Wallet DevOps engineer searched for an AI coding tool and downloaded a tampered version of Homebrew to install it. Binance caught this anomaly, replaced the device, and rotated credentials. But by then, the attackers had learned what the engineer worked on and who else worked on the wallet infrastructure team.
In September, they approached another engineer on a legitimate job platform, posing as a Project Director at another company. The first interview was a live video interview with a fake HR representative, who shared a social media account full of personal photos and videos to build trust. The second interview took place on a popular messaging app, with someone claiming to be the CEO of the same fake company.
Near the end, Engineer B was told to download a “task” onto a work computer. The repository ran malicious code during setup, swapped the legitimate file for a tampered copy, and opened contact with an attacker-controlled server. Binance says the zero-day malware evaded its endpoint protection, and the attackers worked to erase their traces.
On October 20, they used Engineer B’s computer and an internal AI tool to take control of Engineer A’s machine and a third engineer’s, Engineer C. They found a container deployment token on Engineer A’s computer. On October 29, they used it from Engineer C’s computer to deploy a container and run the script that started the theft.
North Korea is frequently linked to hiring fraud
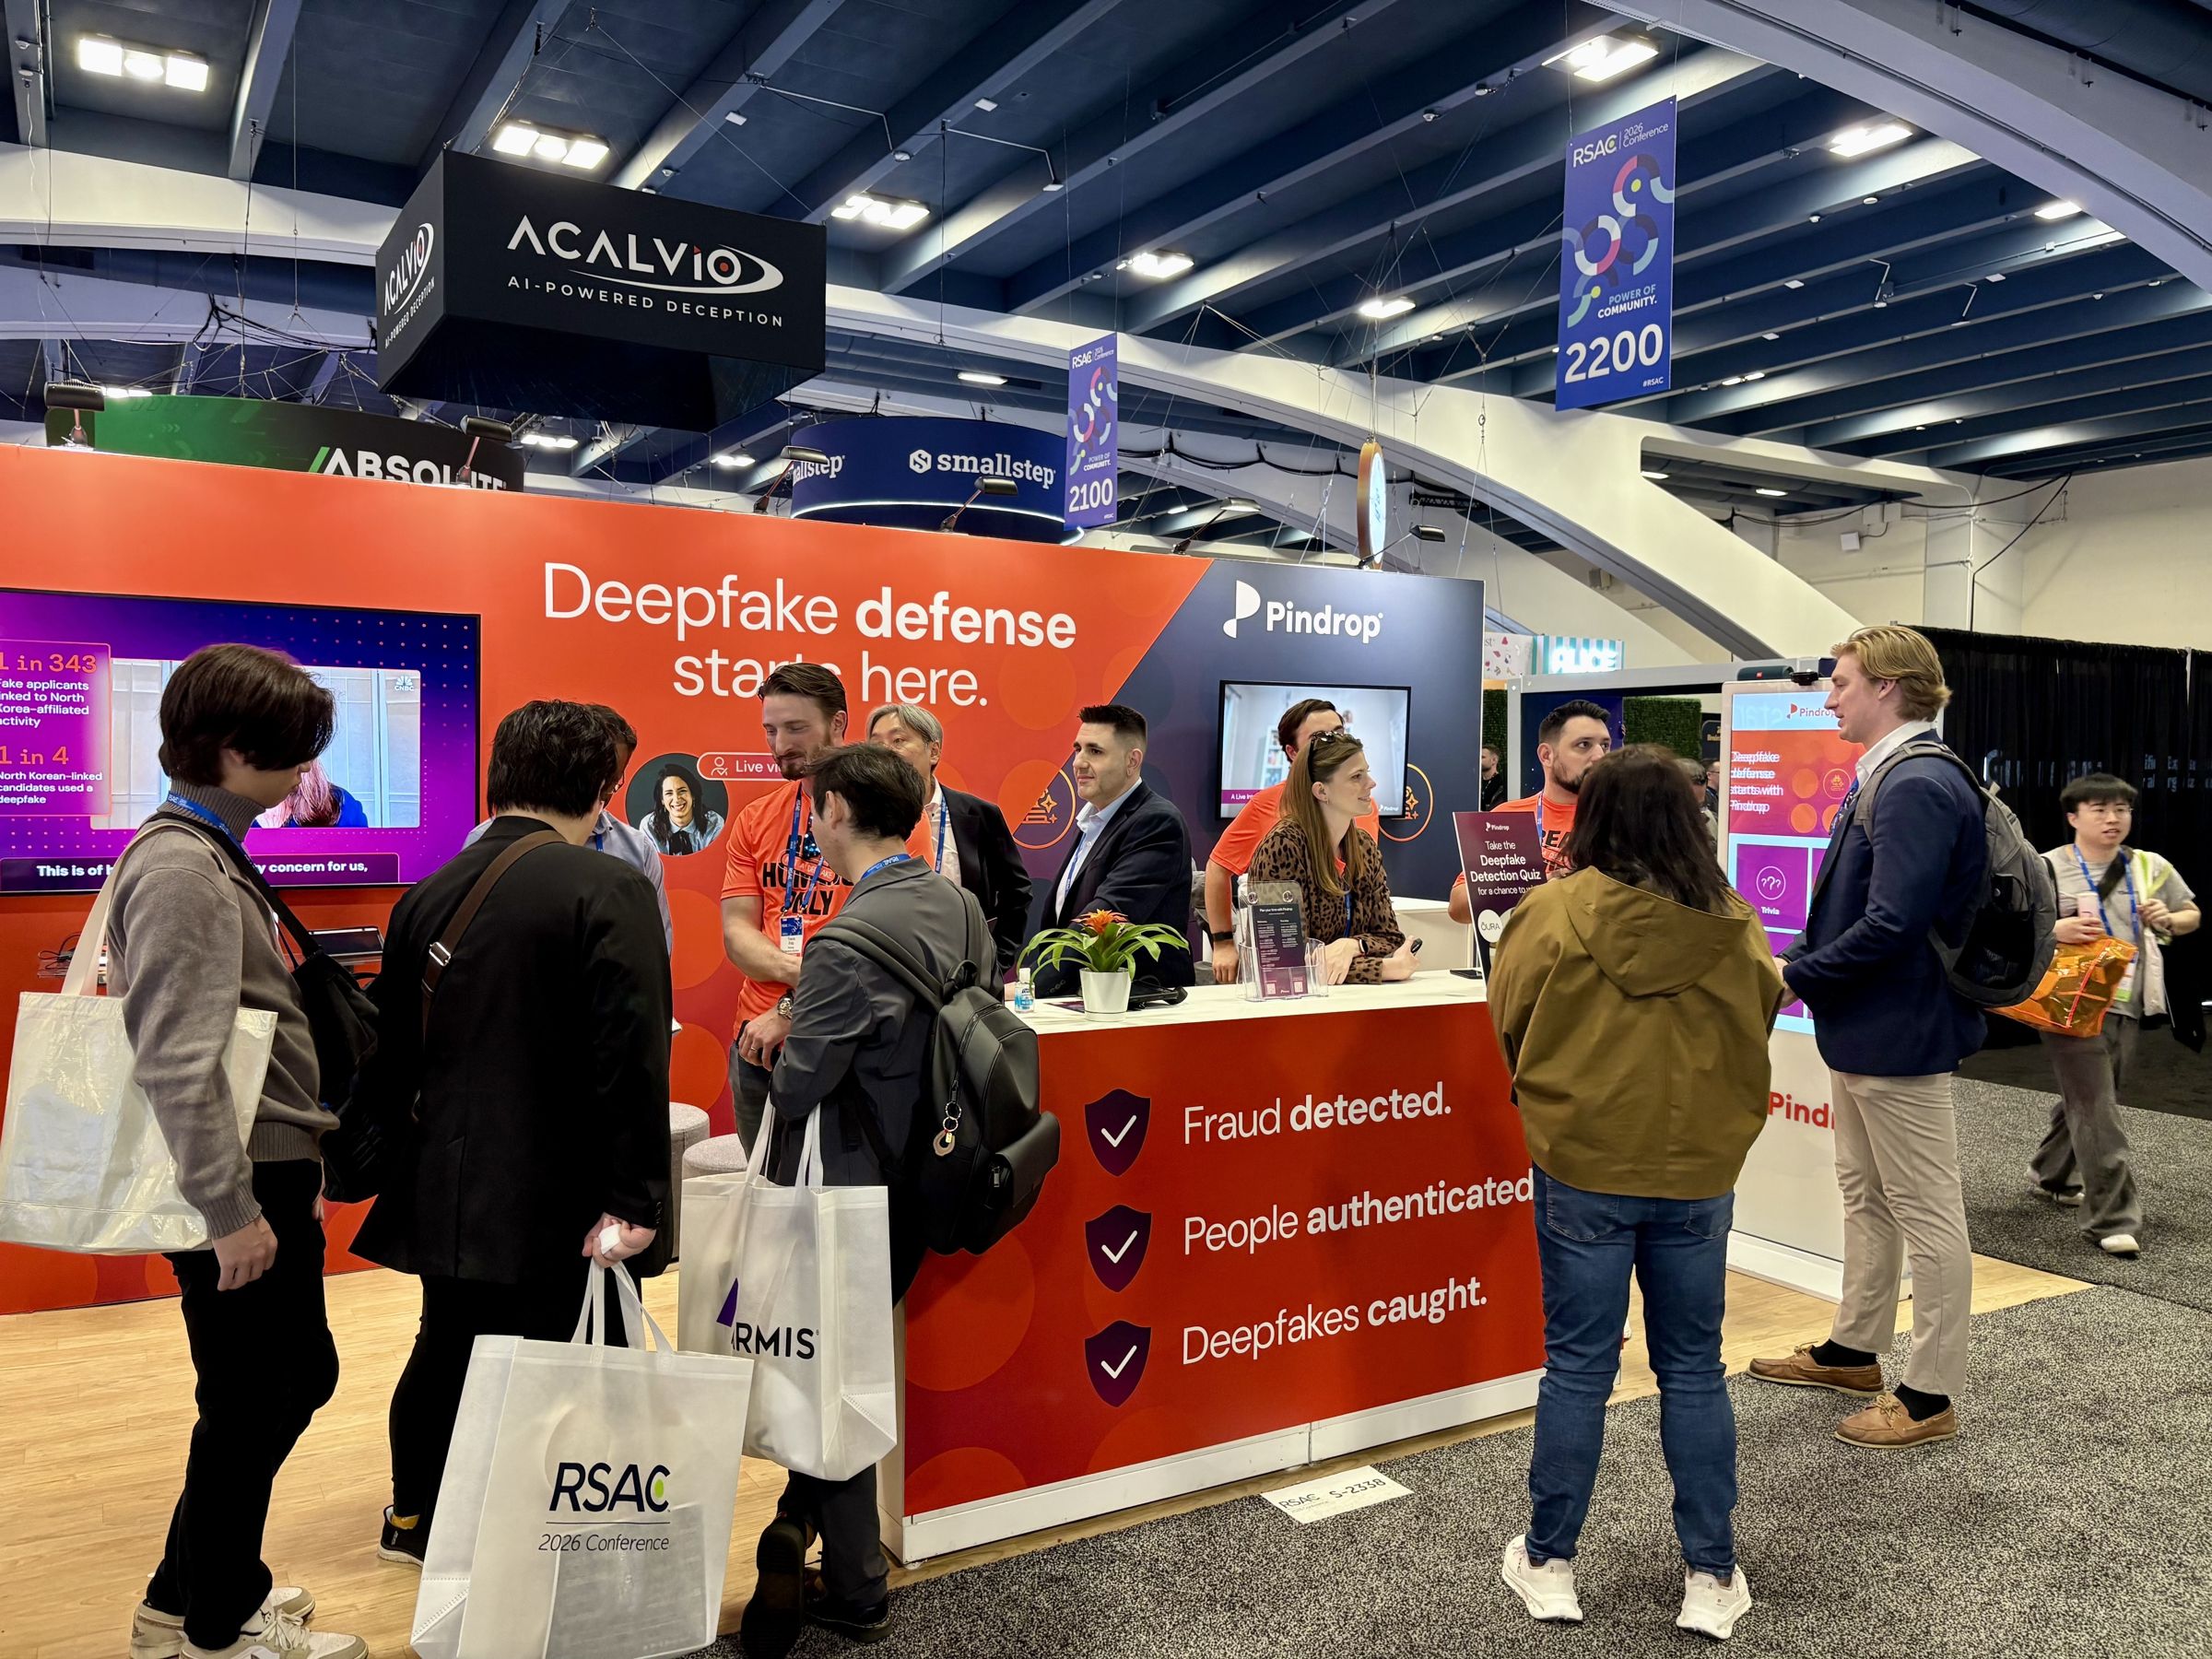
In 2026, Binance says it detected 57 suspected North Korea-linked incidents, including fake job interviews, malicious developer tools, and fake conferencing apps. The FBI and Department of Justice have separately detailed schemes in which North Korean operatives used stolen or fabricated identities to get remote jobs at U.S. companies. In this scenario, the fake person is not the candidate but the recruiter.
Hiring is one door into a larger identity problem. Multi-factor authentication and endpoint tools still matter, but they can’t tell you whether the person on a video call is who they claim, or whether a laptop with a valid login was compromised months ago.
It also undercuts the “weakest link” idea. These attackers researched staff, built personas, and wrote custom malware. A normal employee wouldn’t be able to catch this kind of fraud.
What to change at your own organization
You can't treat every potential employee as a suspect, but you can make the conversations verifiable. Here are four places to start, whether you’re thinking about this from a company or employee perspective:
- Keep outside code off work devices. Coding “tasks” from an unverified source belong in a sandbox or on a personal device, never on a laptop with production access.
- Limit what one device can reach. Apply least privilege, and keep high-risk systems like signing infrastructure separate from everyday development machines. Recheck access after any endpoint compromise.
- Verify identity continuously. Check candidates' identity documents and flag mismatches across résumé, voice, video, and location. Verify again at sensitive moments, like access requests and help desk resets.
- Watch calls for signs of impersonation. Use tools that detect synthetic or manipulated audio and video, and treat a flag as a reason to verify, not a verdict.
Talent acquisition, HR, IT, and security should work from the same fraud and security playbook. Attackers don't respect those org lines, and your controls shouldn't either. The next breach may start with a conversation. Build in the step that checks who's on the other end.
Learn how to detect hiring fraud at your own organization with Pindrop Pulse® for Meetings.
Key results
1%
Text
1%
Text
1%
Text
Lorem ipsum dolor sit amet consectetur. Sit convallis ullamcorper et varius venenatis blandit vitae hendrerit blandit. Hac aenean tellus consectetur elit orci aenean ipsum arcu. Turpis a laoreet sit rhoncus eros penatibus facilisis dolor tempus. Vitae gravida fames nunc dui scelerisque porta nulla ut. Sit mi volutpat ipsum odio nulla sociis.
Lorem Ipsum is simply dummy
Vitae eleifend mi lorem iaculis malesuada sit adipiscing vel. Sit massa ut etiam eu.